
06
AugBy embracing the Japanese Kaizen philosophy of continuous incremental improvement, your AppSec program can evolve […]
30
JulYour DevSecOps pipeline is fast, automated, and built to scale. But is security truly integrated,[…]
29
JulAbout 4 years ago I have joined the OWASP Software Assurance Maturity Model (SAMM) project[…]
17
JulIn this technical article, we will explore how to improve your DevSecOps processes by integrating[…]
11
JunMost security issues in software stem from one simple problem: teams try to fix them[…]
26
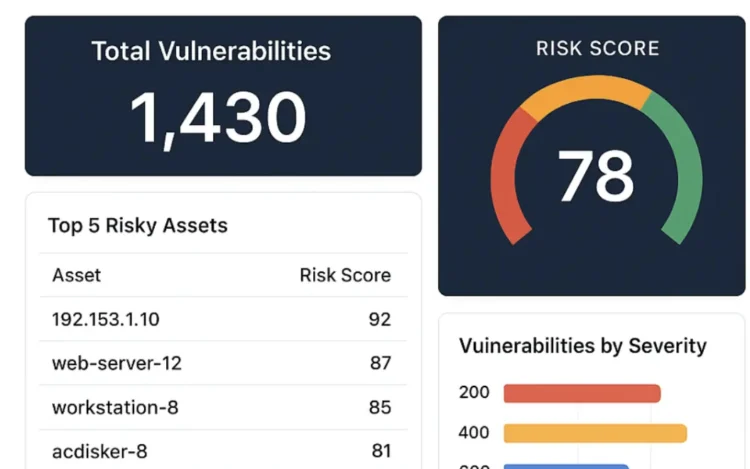
MayYou’ve probably heard the saying, “You can’t manage what you don’t measure.” If you are[…]
24
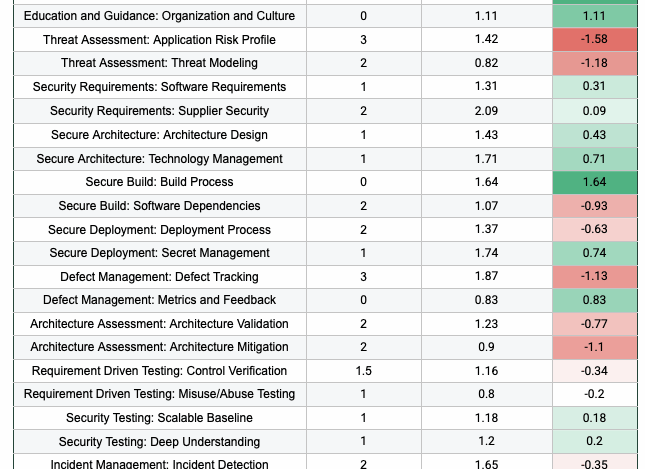
AprOfficial framework, regulation and standard pages mentioned in this article CRA GDPR OWASP SAMM[…]
04
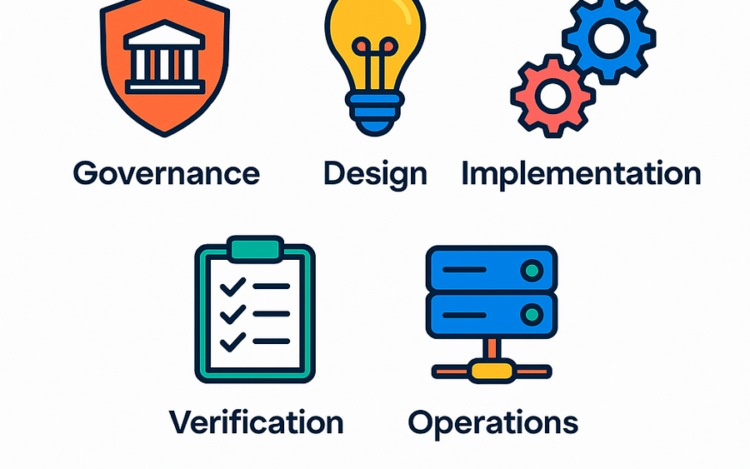
AprModern software development moves fast, and so do the security challenges that come with it.[…]
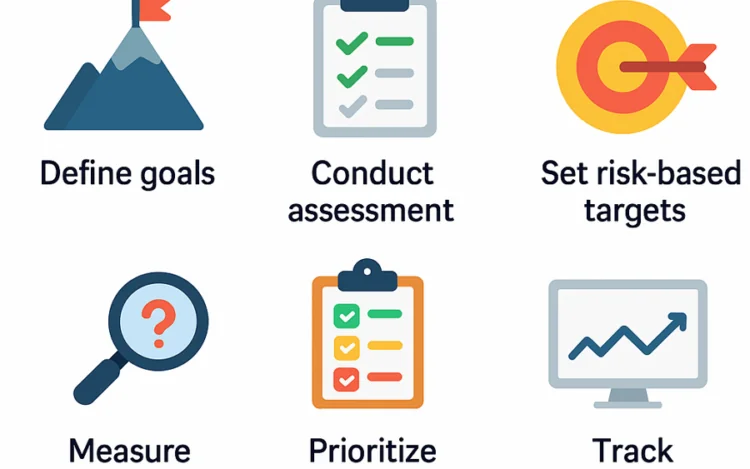
04
AprUnderstanding OWASP SAMM is only the beginning. The real value comes from using it to[…]
07
DecThe U.S. cybersecurity strategy seems to be lightyears ahead of the EU. I strongly believe[…]

29
NovApplication security is a complex discipline. To make things even harder for us, it is[…]
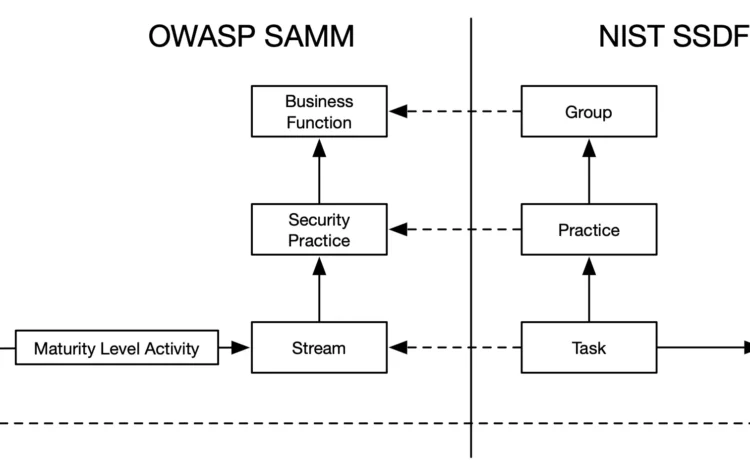
28
NovOver the past year, our SAMMY tool has grown significantly. It now supports not just[…]