Codific
  • Solutions
    • AppSec Management with SAMMY
    • PRC Management with SAMMY
    • Threat Modeling with SAMMY
    • SAMMY Versions
    • Ed-Tech and HR-Tech
      • Secure Video Sharing with Videolab
      • Student Attendance Tracking with Attendance Radar
      • Survey Analysis Automation with SARA
  • Services
    • Consultancy Services
    • OWASP SAMM Assessments
    • Threat Modeling
    • OWASP SAMM Training
    • OWASP SAMM Guidance
  • Customers
    • Zebra Technologies
    • Sigma Software Group
    • Sign In Solutions
    • Kiloverse
    • Approach Cyber
    • All Customer Stories
  • Company
    • Our Story
    • Who We Are
    • Codific @ OWASP
    • Careers
  • Partners
    • Implementation Partners Program
      • Partner Success Story
    • Academic Application Security Program
  • Insights
    • Blog
    • The AppSec Management Podcast
    • Application Security Science
    • Press Coverage
  • Contact
  • Go to SAMMY

AppSec

Home AppSec
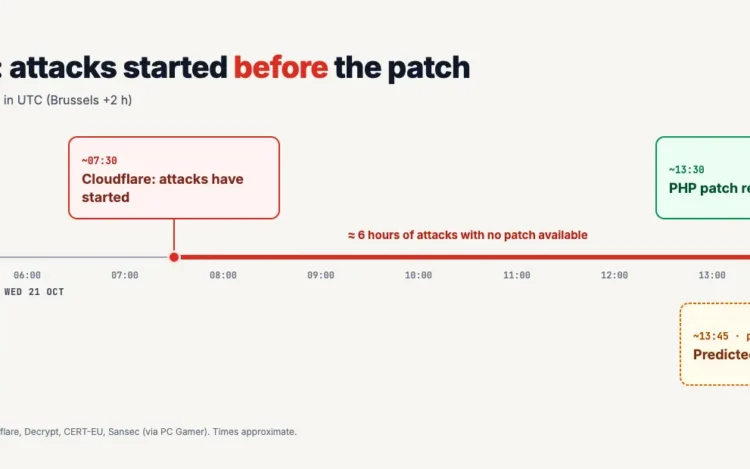
PHP2Shell timeline

26

Oct

Emergency patching in the age of AI: best practices

  • Aram Hovsepyan

In AppSec preparation is 99% of the battle October 20th, PHP.net has published an advanced […]
Read Article
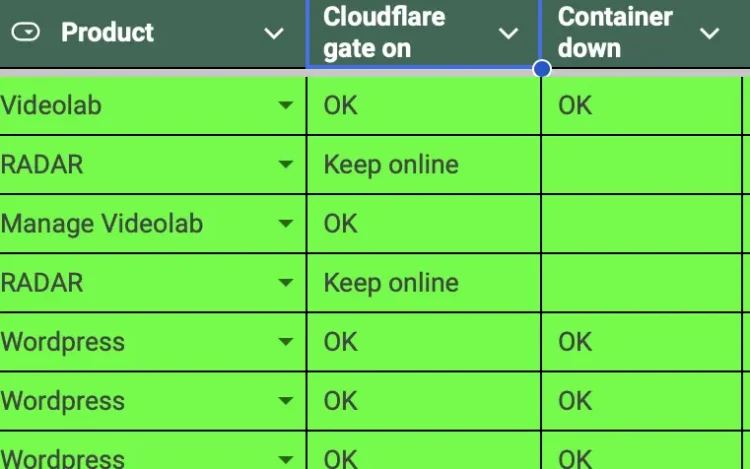
Asset inventory

26

Oct

How Codific handled php2shell

  • Aram Hovsepyan

In short: PHP2shell was considered as a critical event leading to extremely high risk. Handling[…]
Read Article
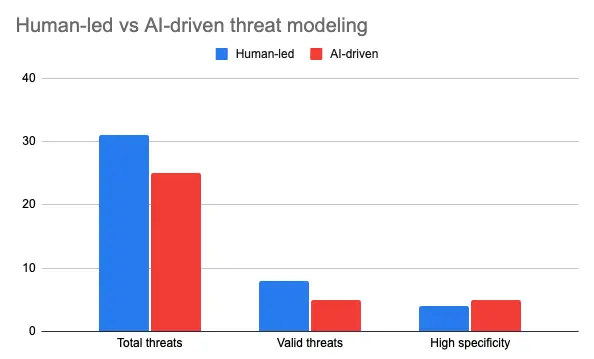
human-led vs ai-driven threat modeling

22

Oct

Human-Led vs AI-Driven Threat Modeling: A Controlled Experiment

  • Aram Hovsepyan

There has been a lot of debate recently about using AI to augment or even[…]
Read Article

15

Oct

Cybersecurity Awareness month: 5 new things to be aware of in the age of AI

  • Michaella Masters

Cybersecurity Awareness month: 5 new things to be aware of in the age of AI[…]
Read Article
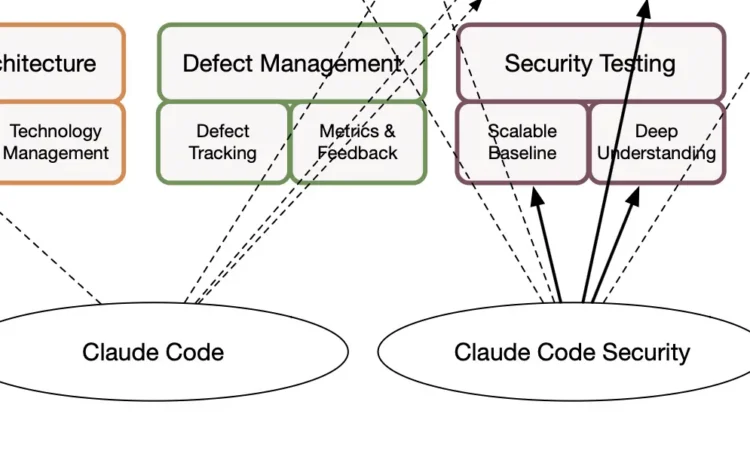
Claude Code Security Excerpt

24

Feb

Claude Code Security: Will AI Disrupt Application Security?

  • Aram Hovsepyan
  • AI, Application Security

Everyone can now write code with Claude and get to production in a weekend. So[…]
Read Article
Secure Controls Framework Illustration

31

Jan

Secure Controls Framework: A Comprehensive Overview

  • Nicolas Montauban
  • Privacy, SCF, Secure Controls Framework, Security

Security programs rarely fail because teams do not care. They fail because the work gets[…]
Read Article
Security scopes

31

Dec

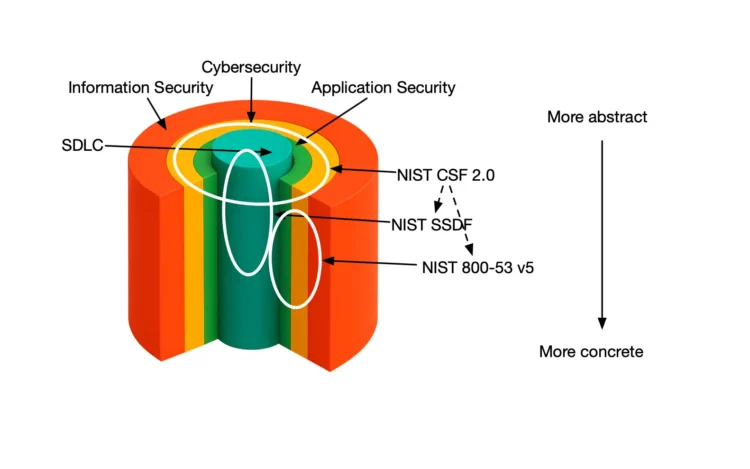
NIST SSDF 1.2 Explained

  • Aram Hovsepyan
  • Application Security, NIST SSDF

For the past couple of decades, organizations have increasingly invested in security. Unfortunately, they often[…]
Read Article

13

Dec

OWASP Top 10 2025 – what it is, what changed, and what to do with it

  • Michaella Masters

If you build or look after web applications, you have probably bumped into the OWASP[…]
Read Article
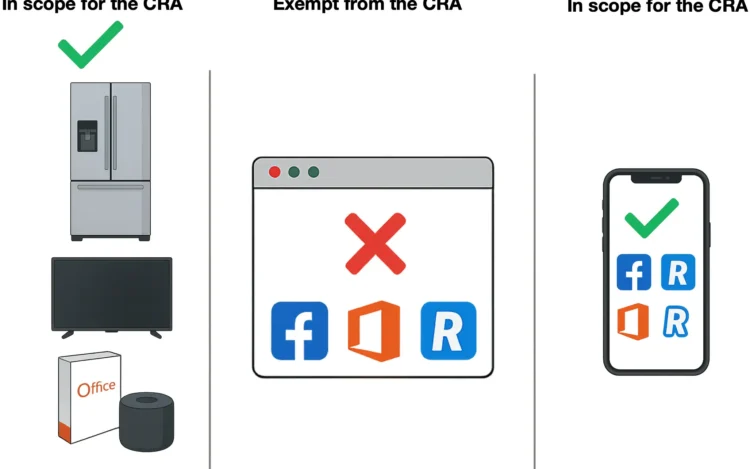
Nearly everything is in scope for the CRA except for SaaS

01

Dec

How to prepare for the CRA

  • Aram Hovsepyan
  • Application Security, Compliance, CRA, Cyber Resilience Act, Cybersecurity

The upcoming Cyber Resilience Act (CRA) is a EU regulation that was published on November[…]
Read Article
OWASP ASVS Blog Illustration for Featured Image

25

Nov

OWASP ASVS: A Comprehensive Overview

  • Nicolas Montauban
  • Application Security, Application Security Management, OWASP, OWASP ASVS

As software systems grow more complex, proving that they are secure has become as important[…]
Read Article
Road illustration of a cybersecurity gap analysis journey

31

Oct

What is a Cybersecurity Gap Analysis? The Role of Mappings

  • Nicolas Montauban
  • Application Security, Cybersecurity, Security Maturity

Most organizations conduct security assessments, yet few turn them into meaningful improvement. Traditional cybersecurity gap[…]
Read Article
Managing application risk with CVE and CVSS driven dashboards

16

Oct

The Realities of AppSec Risk Management using CVE and CVSS

  • Aram Hovsepyan
  • Application Risk Management, AppSec, Common Vulnerability Enumeration, Common Vulnerability Score System

Many organizations treat Common Vulnerabilities and Exposures (CVEs) as first-class citizens. Some even enforce strict[…]

Read Article
Next

Building a simple and safe digital future

This website runs on green hosting - verified by thegreenwebfoundation.org
  • Visit Codific's LinkedIn channel (opens in a new tab)
  • Visit Codific's YouTube channel (opens in a new tab)
  • Spotify

Main Focus

Application Security Compliance Cybersecurity NIST SSDF OWASP OWASP SAMM Privacy by Design SAMM Secure Software Development Security Software security SSDLC

Recent Post

  • PHP2Shell timeline

    October 26, 2026

    Emergency patching in the age of AI: best practices

    October 26, 2026

  • Asset inventory

    October 26, 2026

    How Codific handled php2shell

    October 26, 2026

  • human-led vs ai-driven threat modeling

    October 22, 2026

    Human-Led vs AI-Driven Threat Modeling: A Controlled Experiment

    October 22, 2026

In the Spotlight

  • SAMMY
  • The AppSec Management Podcast
  • Secure Video Sharing with Videolab
  • Attendance Radar
  • SARA
  • Terms & Conditions
  • Imprint
  • Cookie Policy
  • Privacy Statement

Codific • Building a simple and safe digital future 2026. All rights reserved.

Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
View preferences
  • {title}
  • {title}
  • {title}