
25
NovAs software systems grow more complex, proving that they are secure has become as important […]
31
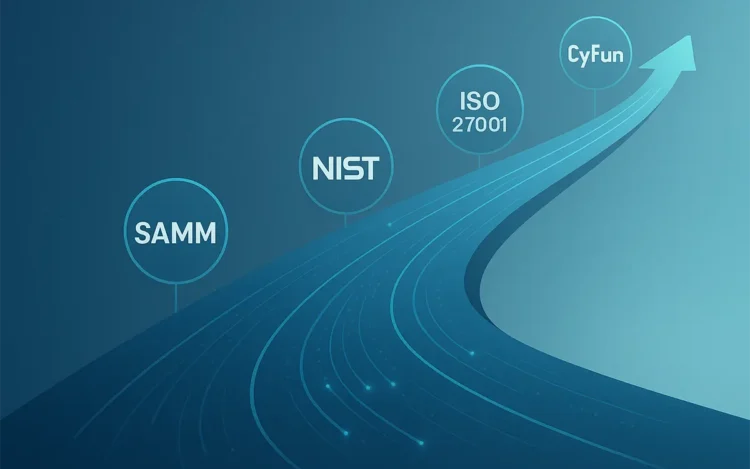
OctMost organizations conduct security assessments, yet few turn them into meaningful improvement. Traditional cybersecurity gap[…]
16
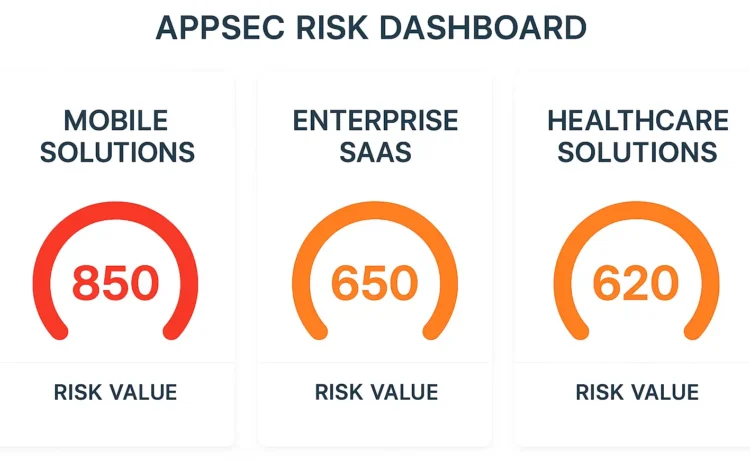
OctMany organizations treat Common Vulnerabilities and Exposures (CVEs) as first-class citizens. Some even enforce strict[…]
20
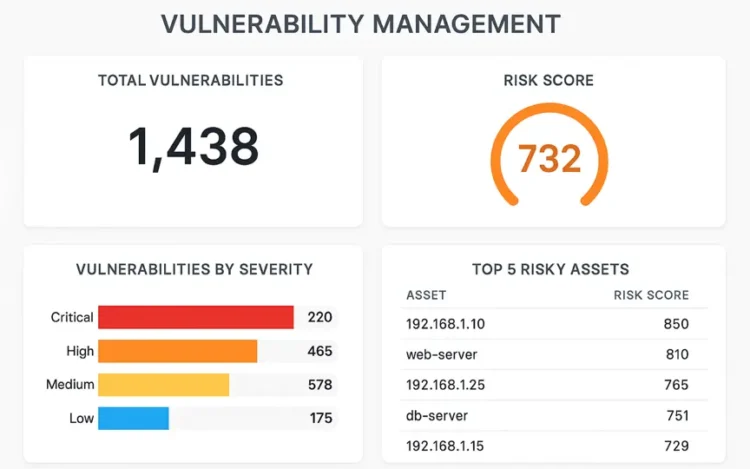
SepApplication security (AppSec) remains one of the toughest challenges modern organizations are facing. Despite heavy[…]
06
AugBy embracing the Japanese Kaizen philosophy of continuous incremental improvement, your AppSec program can evolve[…]
30
JulYour DevSecOps pipeline is fast, automated, and built to scale. But is security truly integrated,[…]
29
JulAbout 4 years ago I have joined the OWASP Software Assurance Maturity Model (SAMM) project[…]
17
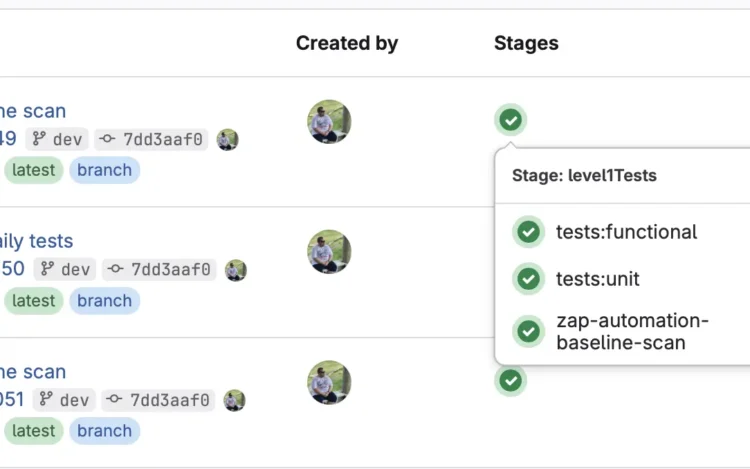
JulIn this technical article, we will explore how to improve your DevSecOps processes by integrating[…]
10
JulThis article contains a variety of different cybersecurity statistics and trends of 2025 and recent[…]
11
JunMost security issues in software stem from one simple problem: teams try to fix them[…]
26
MayYou’ve probably heard the saying, “You can’t manage what you don’t measure.” If you are[…]
24
AprOfficial framework, regulation and standard pages mentioned in this article CRA GDPR OWASP SAMM[…]