
26
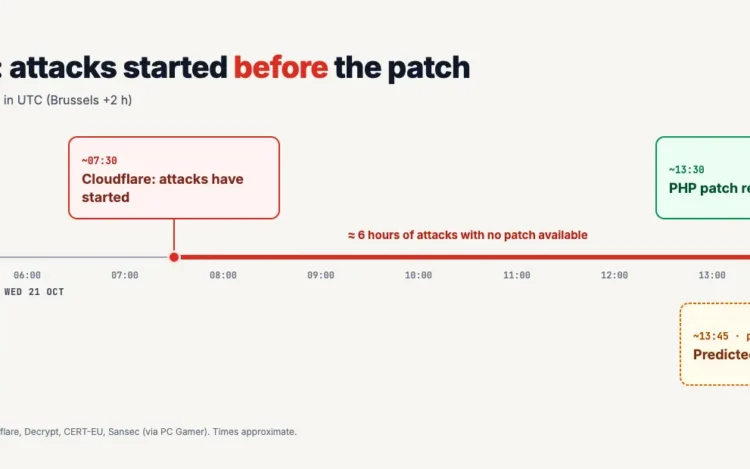
OctIn AppSec preparation is 99% of the battle October 20th, PHP.net has published an advanced […]
15
OctCybersecurity Awareness month: 5 new things to be aware of in the age of AI[…]
31
JanSecurity programs rarely fail because teams do not care. They fail because the work gets[…]
01
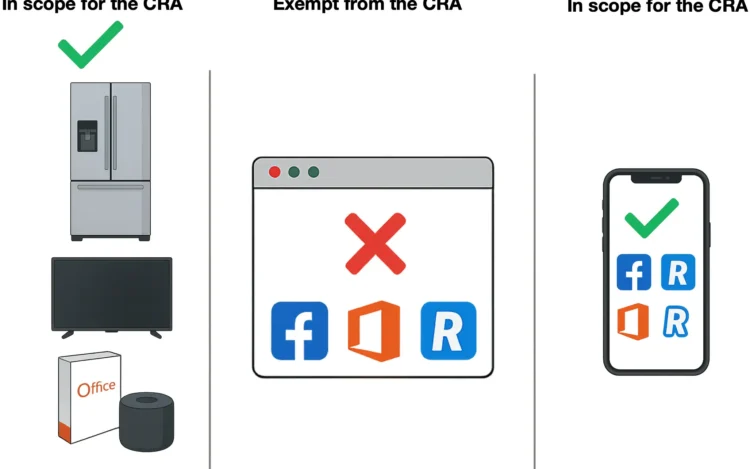
DecThe upcoming Cyber Resilience Act (CRA) is a EU regulation that was published on November[…]
27
NovThe warning shots are over. The NIS 2 Directive is live, and enforcement has begun.[…]
25
NovAs software systems grow more complex, proving that they are secure has become as important[…]
31
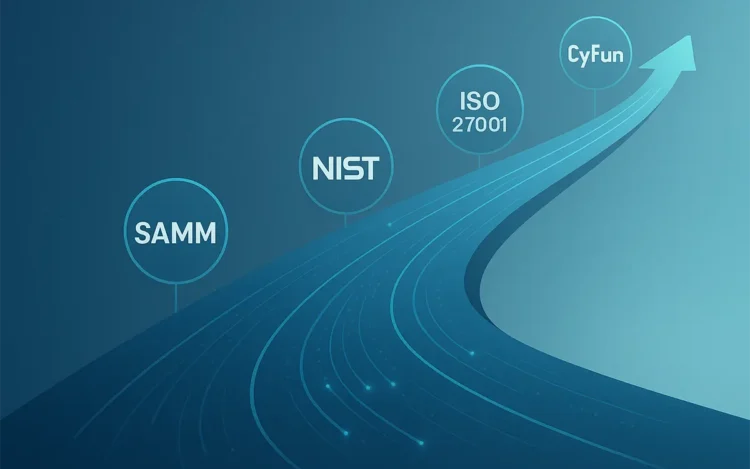
OctMost organizations conduct security assessments, yet few turn them into meaningful improvement. Traditional cybersecurity gap[…]
16
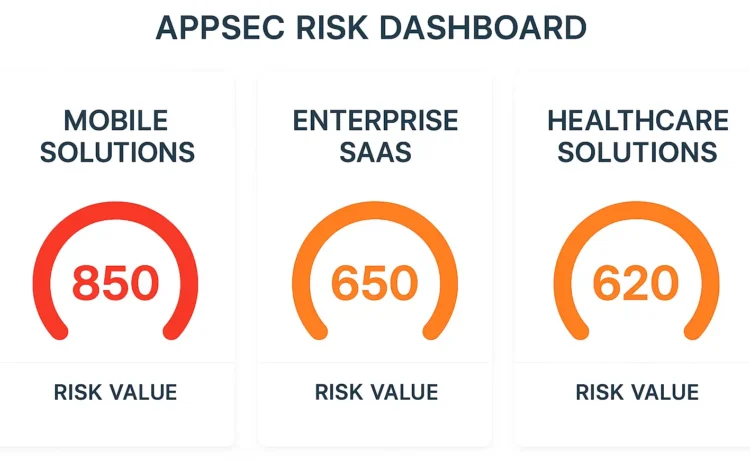
OctMany organizations treat Common Vulnerabilities and Exposures (CVEs) as first-class citizens. Some even enforce strict[…]
06
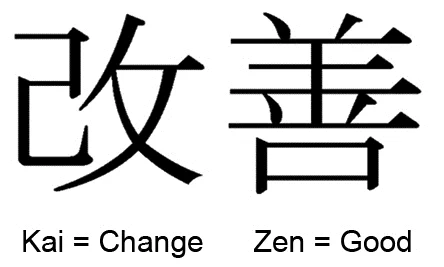
AugBy embracing the Japanese Kaizen philosophy of continuous incremental improvement, your AppSec program can evolve[…]
30
JulYour DevSecOps pipeline is fast, automated, and built to scale. But is security truly integrated,[…]
10
JulThis article contains a variety of different cybersecurity statistics and trends of 2025 and recent[…]
11
JunMost security issues in software stem from one simple problem: teams try to fix them[…]