
Kickstart your
secure SDLC
A hands-on program that turns OWASP SAMM from an abstract framework into a roadmap your team can actually run with. Training and real assessment in one, from the people who help write the standards.
Product security is a cost–benefit
trade-off, not a checkbox
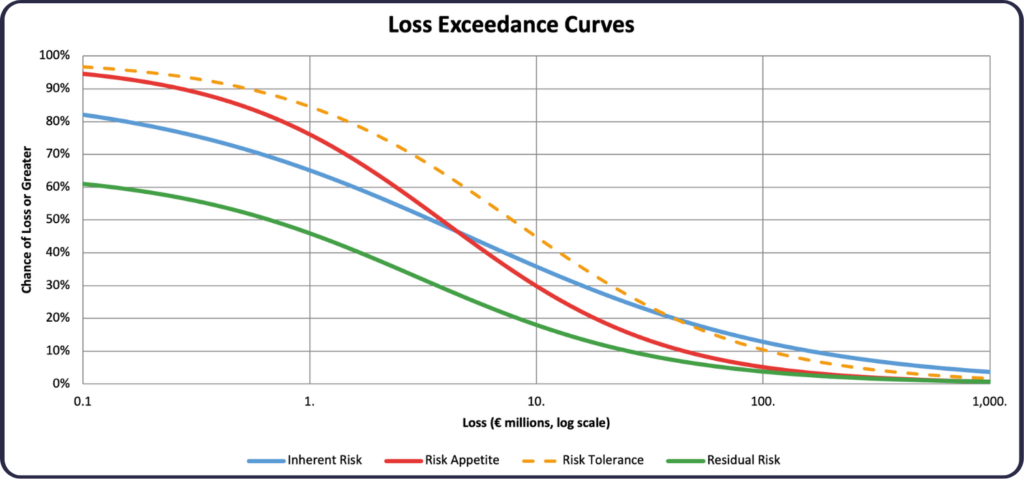
Product security means protecting the confidentiality, integrity and availability of what you build. But security is never absolute; it’s a function of risk. Lack of it hits your bottom line directly, so the real question isn’t “are we secure?”
It’s: how much security do you actually need to keep residual risk below what’s acceptable, at a cost that makes sense?
Tooling alone won’t save you.
For two decades, tooling has been the industry’s default answer to security challenges. Today the same hope is pinned on AI: that it will write secure code, find vulnerabilities and patch them automatically. Early research suggests that’s optimistic, and even where it isn’t, code is only part of the story. You can’t code your way out of a bad design. Security assurance is about people, process and tools, in that order.
That’s why it takes a holistic approach.
Start with understanding risk, then build the right controls to manage it – that’s where a systematic framework like OWASP’s Software Assurance Maturity Model (SAMM) comes in, and exactly what this workshop is built around.
A workshop built around your product
This is different from a standard assessment. We translate the abstract SAMM model into your team’s world: their terminology, their architecture, their day-to-day process.
01
Training, plus a real assessment
We assess your actual product, or an entire line of business, as we teach, so every concept lands in a context your team already recognizes.
02
Speaks your team’s language
Terminology, expectations and concrete next steps for your scenario, not abstract maturity-model jargon nobody uses again after the workshop.
03
Built on OWASP SAMM, CRA-ready
Delivered against the industry-standard framework, with an optional gap analysis against the EU Cyber Resilience Act, whose technical obligations map directly onto SAMM.
Five sessions.
One holistic view of your secure SDLC.
Each core session runs around 90 minutes and can be scheduled to fit your team’s calendar.
New to the topic? We start with a 60-minute introduction first.
OPTIONAL · 60 min
Introduction to Product Security
For teams who haven’t been through it before: the key challenges in application security, common pitfalls in tooling and process, and what a holistic, best-practice approach looks like.
01 Risk, Governance & Knowledge
Security starts with understanding risk from an organizational perspective, then aligning policies, standards and compliance
around it.
02 Architecture & Secure Design
You can’t code your way out of a bad design – no AI coding assistant included. Focus on secure architecture and architectural threat modeling.
03 Vulnerability Management
Vulnerabilities keep growing explosively. Start from clearly defined security requirements so triage stops being a full-time job.
04 Secure Build & Deploy
Your DevOps pipeline is automation-heavy but not trivial to secure; and can be an attacker’s way in.
05 Opterations
Keeping confidentiality, integrity and availability intact for the life of the product and its data.
CLOSING · 60 min
Tailored Roadmap Recommendations
A closing presentation with a detailed, prioritized set of recommendations for the product or team we focused on, tailored to your business landscape and risk.
What you walk away with
Beyond the sessions themselves, the workshop leaves your team with something concrete.
A roadmap, not a report
A prioritized, risk-based roadmap tailored to your product or business line, not a generic maturity score.
A team fluent in SAMM
Your team leaves speaking the same language as the framework: terminology, expectations, and how to apply them day to day.
Compliance clarity
An optional CRA gap analysis shows exactly where you stand against the EU Cyber Resilience Act’s technical obligations.
Ready to act on your roadmap?
We'll help you implement it.
Every product, team and organization ends up with a different roadmap, but a handful of work packages consistently deserve priority. Our team, led by Dr. Aram Hovsepyan and Brian Glas, can help you deliver them.
Policies & Processes
Review your existing security policies against legal, regulatory and compliance obligations, then draft an updated, prioritized set of policies and standards.
Risk Assessment Methodology
A consistent, repeatable methodology for identifying, scoring and prioritizing risk, aligned to your new policies and standards.
Threat Modeling Methodology
Our tiered, control-based methodology, backed by our SAMMY tool with AI-assisted threat generation, replaces “what could go wrong?” brainstorming with structure.
Security Requirements Framework
A lightweight requirements framework mapped to OWASP ASVS 5.0 and NIST SP 800-53, harmonized with your existing policies.
Code Signing
From key custody and approval gates to verification enforcement: a tailored code-signing solution, plus hands-on migration support.
Guidance from recognised leadersin application security
Dr. Aram Hovsepyan
Founder & CEO, Codific · PhD, Application Security
Aram leads the workshop’s risk and architecture sessions. He has spent over 15 years in application security as a researcher, industry expert and core contributor to the OWASP SAMM project, and is a founding board member of OWASP EU.
He holds a PhD in application security from DistriNet KU Leuven, and his work on refining the LINDDUN privacy engineering methodology has been incorporated into both ISO and NIST standards.
Brian Glas
Application Security Leader · VP of Consulting Services
Brian brings two decades of application security practice to the vulnerability management and operations sessions, as an engineer, program leader and consultant, and is a long-standing contributor to the OWASP community.
He is a project lead on the OWASP SAMM project and the SAMM Benchmark, and a core contributor to the OWASP Top 10 (2017, 2021 and 2025).
COMPLIANCE
Your CRA obligations, already inside the framework
Our team is well-versed in the EU Cyber Resilience Act, both technically and legally. Its technical obligations fit elegantly as a subset of OWASP SAMM, so a SAMM-based workshop doubles as CRA preparation, not a separate project.
Ready to kickstart your secure SDLC?
Tell us about your product, team and timeline. We’ll get back to you to scope the workshop and find a schedule that works.
✓ 5-part workshop, delivered live to your team
✓ Tailored to your product or an entire line of business
✓ Optional CRA gap analysis included in scoping