
Threat Modeling with SAMMY Shift from legacy GRC to engineering-led Product Risk and Compliance (PRC). [...]
12
Feb
Choose the right SAMMY for your security program Why multiple versions Organizations differ in scale, [...]
13
Aug
“Cyber serenity to society” is more than a catchy tagline, it’s a high‐stakes promise. Approach Cyber, a [...]
29
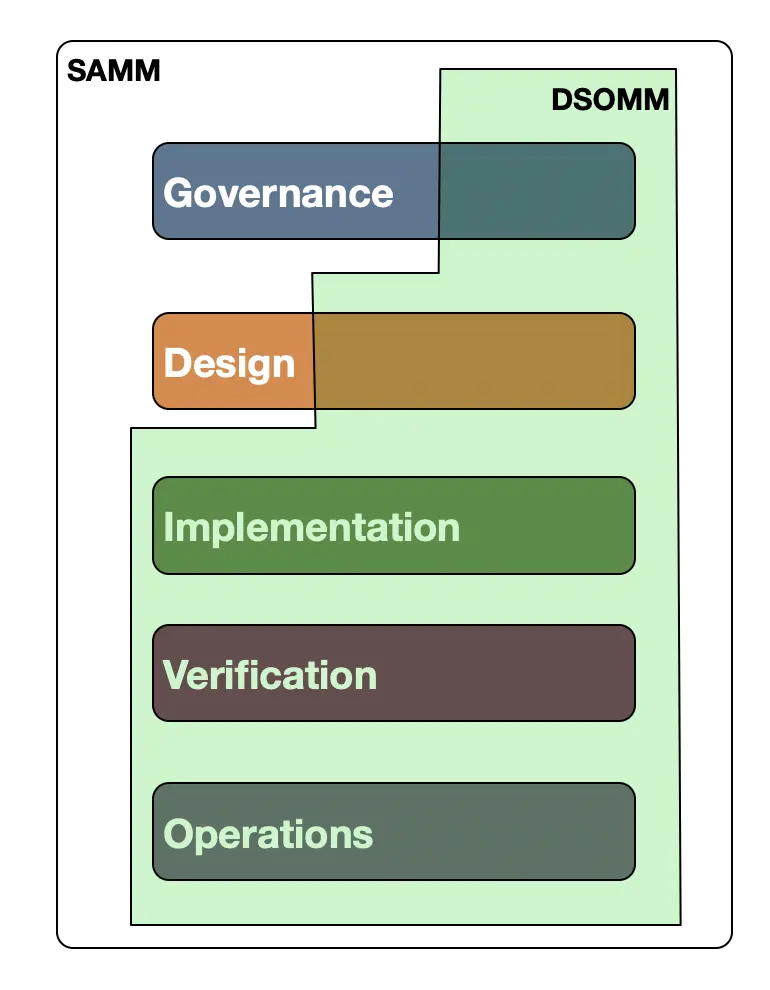
JulAbout 4 years ago I have joined the OWASP Software Assurance Maturity Model (SAMM) project […]

04
AprModern software development moves fast, and so do the security challenges that come with it. […]
04
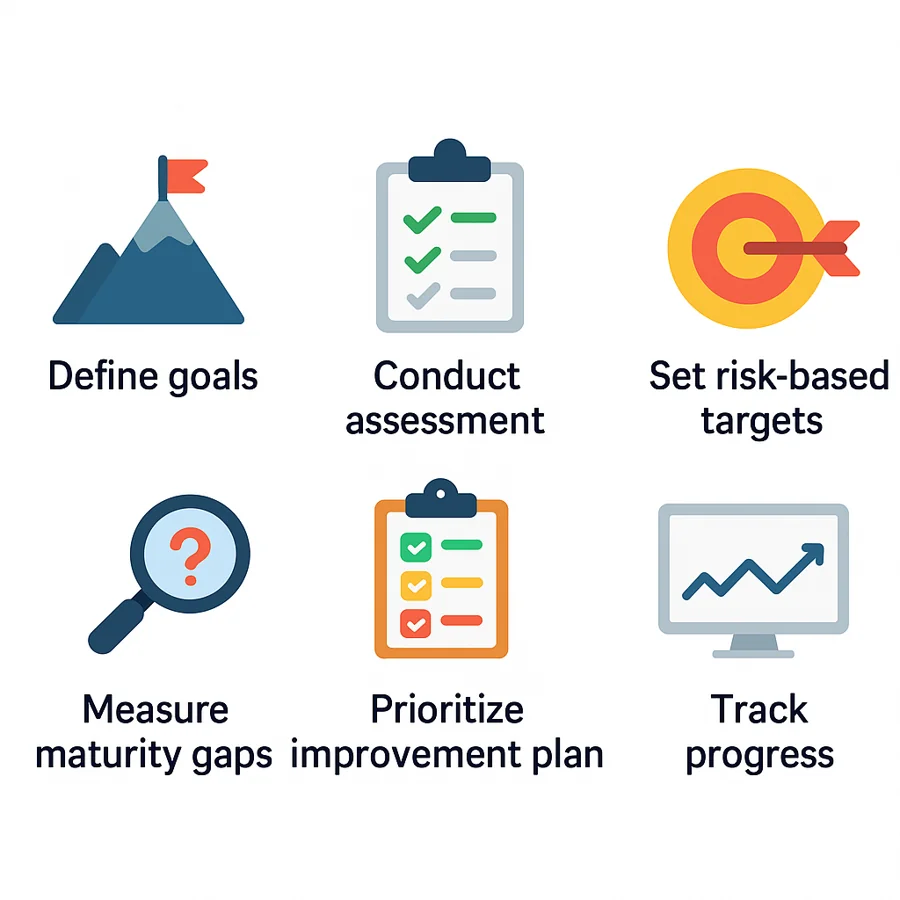
AprUnderstanding OWASP SAMM is only the beginning. The real value comes from using it to […]
31
Mar
Manage your AppSec with SAMMY is a PRC management tool that connects maturity, control and [...]
15
Jan
Your Guide to OWASP SAMM: Insights and Best Practices The OWASP Software Assurance Maturity Model (SAMM) is a powerful tool for improving software security practices. It provides clear steps and a structured approach, enabling teams to assess their current security posture and build better strategies. Our OWASP SAMM Guidance page is here to help you make the most of this framework. It includes practical tips, expert advice, and useful resources to guide you through implementing OWASP SAMM in your organization. 24 Feb AppSec, SAMM Claude Code Security: Will AI Disrupt Application Security? February 24, 2026 AI, Application Security Everyone can now write code with Claude and get to production in a weekend. So we have solved the coding challenges. Time to fire the tech team. As of last week, Claude Code Security has also supposedly solved the application security challenges. There goes the AppSec team as well. Right? Neither idea[...]
28
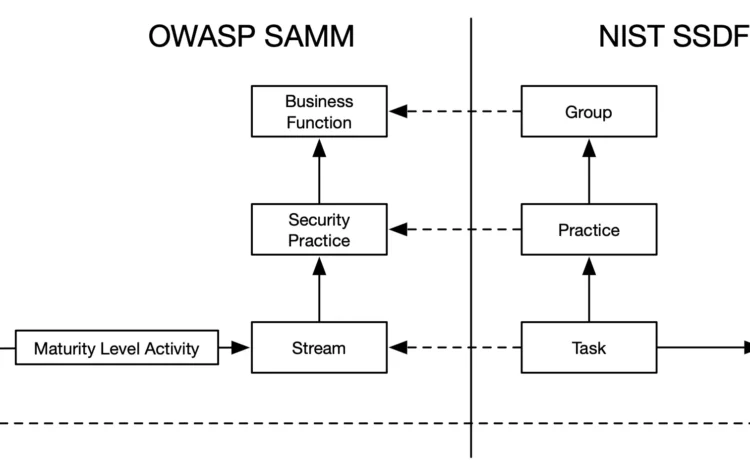
NovOver the past year, our SAMMY tool has grown significantly. It now supports not just OWASP Software Assurance Maturity Model (SAMM) but also many other frameworks and standards. Whether you need a cybersecurity framework, quality framework, maturity model, or compliance standard, SAMMY unifies them all. This versatility often raises a key question: “Which framework is best for an application security program?” OWASP SAMM stands out, but what about Building Security In Maturity Model (BSIMM) or NIST Secure Software Development Framework (SSDF)? SAMM looks excellent on paper, but SSDF comes from NIST, a highly respected organization. Meanwhile, BSIMM is popular among large enterprises. I have already written a blog on BSIMM vs SAMM. BSIMM is not cheap and even if your organization has the budget, SAMM is likely a better pick. In this post, I will focus on comparing OWASP SAMM and NIST SSDF. Key Takeaways Reputable Frameworks: Both SAMM and SSDF[…]
28
NovWhether you are getting started with OWASP SAMM assessments at your organization, or you are starting to do SAMM assessments for your clients, there are lots of resources scattered around the internet that provide guidance and practical tips. On this page we gather the most valuable of these OWASP SAMM resources: The Whitepaper on effective SAMM Assessment Strategies: This whitepaper was created in the context of Global AppSec 2024 in Lisbon, it is a collaboration between Toreon and Codific. The paper is written by professional SAMM assessors and OWASP SAMM core team members, specifically from their practical experience running SAMM assessments at companies large and small. The paper covers: General introduction to SAMM Assessment tools Assessment types Interview planning The interview process Post interview validation Sample interview questions And much more Download the white paper on Effective SAMM Assessment strategies. The podcast on SAMM assessments Also in[…]
02
NovOWASP Software Assurance Maturity Model (SAMM) is one of the only comprehensive frameworks available for application security program management. Aside from BSIMM, there’s not much else around. Moreover, SAMM is open-source, making it accessible to everyone with zero barriers to entry. However there’s a catch: implementing OWASP SAMM comes with a learning curve. Beginner and even intermediate users seem to struggle with certain aspects of the model. Based on my experience, users have the hardest time figuring out: How to deal with quality criteria (or the “definition of done”) and what they mean; How to come up with a meaningful prioritization for the improvement roadmap; What type of evidence is required for demonstrating “compliance”; How to interpret the model for domains other than web application development; How can SAMM help for a smaller company. In this blog, I will offer 12 foolproof ways to ensure your SAMM assessments and improvement[…]
29
Oct
How to get started with ISO 27001 compliance management with SAMMYWatch this video on YouTube ISO27001 The ISO27001 module in SAMMY covers the controls outlined in ISO27001:2022 annex A. These are all the things you need to cover to demonstrate compliance with ISO27001. You can use SAMMY in preparation of a 27001 certification or as a continuous management tool beyond certification. The ISO27000 family The 27001 standard is part of the 27000 family which is established by the International Organization for Standardization (ISO) and covers information security management. Find out more about the ISO27000 family here. What is included in the ISO27001 controls? The controls are divided into four sections: Organization People Physical Technological Where to find ISO27001 management in SAMMY? The default model in SAMMY is OWASP SAMM. In order to start an ISO27001 management instance you must login and go to scopes, where you create a DRP scope.[...]